JUST LEARNING - HACKING - OS
WHAT'S NEW?
Loading...
Showing posts with label Hacking. Show all posts

Become Anonymous & Browse the Internet Safely


We all know about PRISM. The Surveillance Program allowing the U.S Government to access private user information. Such as, Google Searches, Tweets, Facebook Posts, Private Images, and other private user data. "Hiding" yourself can be very difficult, but it is possible. I'm here to show you How to Become Anonymous & Browse the Internet Safely.

1. Deleting Old Email & Social Accounts.

Removing your real identity from social media sites and website databases is important when keeping your real identity Anonymous. If that is not possible (for instance, email accounts or other) change the name of said account to a random name, thus making it seem like a different person. (If your email is something like: "JonDoe123@email.com" then deleting the account would be better for you)

2. Worry Free Site Browsing

Using a normal browser such as, Firefox, Chrome, Safari, Opera, and others won't work in terms of staying anonymous. These browsers don't encrypt the users data, leaving it open to phishers and keyloggers. If you want to stay anonymous, then you need to download Tor. Tor allows full privacy and encryption. It has many features, some include,
  • Automatic IP Changing (allowing you to make accounts without being traced)
  • NoScript (disallows certain "suspicious" scripts and cookies from showing and saving your data)
  • Anonymous Networking (allowing encrypted browsing)
  • and many more...
Tor also includes a cracked version of Mozilla Firefox, all plugins included. The downside to Tor is that, it disables mandatory plugins such as, Flash, Java, and other important scripts. These can be re-enabled by installing them manually in the Tor Directory.

3. Precautions for Signing Up on Website's

If you're like me and like to use sites like, Gmail, YouTube, Twitter, and others, then you'll need to use a Fake Name, Fake Date of Birth, and Fake Profile icon. These factors are the most important when masking your real identity. Using your creativity can benefit you most of the time, but if you can't think of a Name, Username or Password then Name Generators can do the trick. Websites like:


All of these can benefit you when making a new Email, YouTube Account, Twitter, or even Facebook.

Please Note

Use these tips in line of other tips such as, Encrypting your files, passwords and others.


P.S This was my first post here so please be gentle with criticism.

Top 10 Best Books For Learning Hacking 2016

Top 10 Best Hacking Books

Best books for learning hacking: As you all know that a lot of teenagers want to turn out to be a “HACKER“. However, hacking isn’t a simple task. Learning Ethical hacking shouldn’t be an easy task you need to learn many Hacking Books after which implement these ideas or strategies. Then invent new methods to grow to be an ethical hacker.
Hacking Is Not A Crime; It Is An Art
If you want to become ethical hacker then here is a good useful resource for you ! Sure, here is handpicked the collection of Best books for learning hacking edition with hundreds of newest hacking tutorials. If you wish to learn ethical hacking then just download hacking books from below and start exploring the Hacking World.

1.     THE HACKER’S UNDERGROUND HANDBOOK

This book will take you from the core to the top. It can inform you learn how to hack in simple steps. All the things are introduced in an easy and efficient method. It’s a nice source for the newbie who wish to become a Hacker. This can set up a Hacker’s Mindset on you.
The following Features include in this book:

·        You’ll be taught all of the hacker underground tips and learn to use them in real-world situations.
·        You may be put into a hacker mindset and be taught to suppose like a Hacker.
·        By studying how a hacker thinks and acts, it is possible for you to protect yourself from future hack attacks.
·        You’ll acquire knowledge nonexistent to 99.9% of the people in the world!
·        This Underground handbook may get you interested in pursuing a career as an Ethical Hacker.
This book is of great value for all those that have a dream to become a Hacker.

2.     HACKING FOR DUMMIES

There may be certainly no shortage of books on this genre- Counter Hack, Hack Attacks Revealed and the best-selling Hacking Exposed (and all of its spin-offs) have covered this information in exhausting detail. What sets this book aside is that it doesn’t assume you’re already a CISSP or network security analyser. Being a “For Dummies” book signifies that it’s written from the idea that you just don’t know something and the knowledge is written in plain English and in terms that even a youngster may often understand.

3.     OFFICIAL CERTIFIED ETHICAL HACKER  STUDY GUIDE

Kimberly Graves, CEH, CWSP, CWNA, CWNP has over 15 years of IT experience. She is a founder of Techsource Network Options, a network, and safety consulting group situated within the Washington, DC area. She has served as subject matter knowledgeable for a number of certification programs together with the Certified Wireless Network Professional (CWNP) and Intel Certified Network Engineer programs and also has developed the course materials for the Department of Veteran Affairs, USAF, and the NSA. The Certified Ethical Hacker examination is quickly becoming some of the popular security certifications offered today. Candidates much prove their ability in not only figuring out security risks from all levels but also how to tackle these risks. This book provides a concise, simple to follow the strategy to this difficult exam.
The following Features include in this book:
·        Introduction to Ethical Hacking, Ethics, and Legality
·        Footprinting and Social Engineering
·        Scanning and Enumeration
·        System Hacking
·        Trojans, Backdoors, Viruses, and Worms
·        Sniffers
·        Denial of Service and Session Hijacking
·        Web Application Vulnerabilities , Hacking Web Servers and Web-Based Password Cracking Techniques
·        SQL Injection and Buffer Overflows
·        Wireless Hacking
·        Physical Security
·        Linux Hacking 177
·        Evading IDSs, Honeypots, and Firewalls
·        Cryptography
·        Penetration Testing Methodologies

4.     WEB HACKING ATTACK AND DEFENSE

The book provides you details about  how Web hacking happens and teaches you enhanced ability at developing defenses in opposition to such Web attacks. Technologies lined within the book include Web languages and protocols, Web and database servers, payment systems and shopping carts, and also added critical vulnerabilities related to URLs. This book is a virtual battle plan that may make it easier to identify and eliminate threats that would take your Web site offline.
Whether it’s petty defacing or full-scale cyber robbery, hackers are transferring to the Web along with everyone else. Organizations using Web-based business applications are frequently affecting risk. Web Hacking: Attacks and Defense is a powerful guide to the most recent info on Web attacks and defense.
The following Features include in this book:
·        Overview of the Web and what hackers go after
·        Complete Web application security methodologies
·        Detailed analysis of hack techniques
·        Countermeasures
·        Cyber graffiti and Web site defacement
·        E-Shoplifting
·        Database access and Web applications
·        Java™ application servers; tips on how to harden your Java™ Web Server
·        Impersonation and session hijacking
·        Buffer overflows, and the most wicked of attacks
·        Automated attack instruments and worms
Appendices include a listing of The Web and the database ports, cheat sheets for a remote command execution, and source code disclosure techniques and so on.

5.     GRAY HAT HACKING

This book is very helpful for both beginners and professionals. It provides the reader detailed knowledge of penetration testing. It also has chapters on Linux and windows exploits.
The following Features include in this book:
Introduction to Moral Disclosure,
·        Penetration Testing and Tools ,
·        Exploits 101,
·        Vulnerability Analysis,
·        Malware Analysis

6.     HACKING WIRELESS NETWORK WITH DUMMIES

Today wireless networks are everywhere.
The following Features include in this book:
·        Perform ethical hacks without compromising a system
·        Combat denial of service and WEP attacks
·        Understand how invaders think
·        Recognize the effects of various hacks
·        Protect against war drivers and rogue devices
(to be continued)


All these tools come bundled in pentesting Linux distro’s such as Kali Linux or BackBox, so we’d certainly recommend that you install an appropriate Linux hacking box to make your life easier – not least because repositories are (automatically) updated.


Used to Scan Ports and Map Networks - and a whole bunch more!
nmap tools


Nmap is an abbreviation of 'Network Mapper', and it's very well known free open source hackers tool. Nmap is mainly used for network discovery and security auditing. Literally, thousands of system admins all around the world will use nmap for network inventory, check for open ports, manage service upgrade schedules, and monitor host or service uptime. Nmap, as a tool uses raw IP packets in creative ways to determine what hosts are available on the network, what services (application name and version) those hosts are providing information about, what operating systems (fingerprinting) and what type and version of packet filters/ firewalls are being used by the target. There are dozens of benefits of using nmap, one of which is that fact that the admin user is able to determine whether the network (and associated nodes) need patching. Nmap's been featured in literally every hacker movie out there, not least the recent Mr. Robot series. It's also worth mentioning that there's a GUI version of Nmap called 'Zenmap'. We'd advise you to learn using Nmap (i.e. the 'command line') then rotate into Zenmap when you are feeling all confident.

Metasploit Penetration Testing Software | Free & Paid
Vulnerability Exploitation Tool

The Metasploit Project is a hugely popular pentesting or hacking framework. If you are new to Metasploit think of it as a 'collection of hacking tools and frameworks' that can be used to execute various tasks. Widely used by cybersecurity professionals and ethical hackers this is a tool that you have to learn. Metasploit is essentially a computer security project (framework) that provides the user with vital information regarding known security vulnerabilities and helps to formulate penetration testing and IDS testing plans, strategies and methodologies for exploitation. There's a ton of incredibly useful Metasploit information out there and we hope that the books that we've chosen go someway to help you on your journey, not least if you are a beginner just starting out and looking for beginners tutorials in how to use Metasploit.

THC Hydra | Free
Password Cracking Tool

We've purposely placed THC Hydra underneath John The Ripper because they often go 'hand-in'hand'. THC Hydra (we've abbreviated to simply 'Hydra' throughout our site) is a hugely popular password cracker and has a very active and experienced development team. Essentially THC Hydra is a fast and stable Network Login Hacking Tool that will use dictionary or brute-force attacks to try various password and login combinations against an log in page. This hacking tool supports a wide set of protocols including Mail (POP3, IMAP, etc.), Databases, LDAP, SMB, VNC, and SSH. Take a look at John the Ripper as well.


Wireshark | Free
Web Vulnerability Scanners


Wireshark is a very popular pentesting tool and for over a year it was not included on our list, however, by popular demand we added it in late June 2016. Wireshark essentially captures data packets in a network in real time and then displays the data in human-readable format (verbose). The tool (platform) has been highly developed and it includes filters, color-coding and other features that lets the user dig deep into network traffic and inspect individual packets. If you'd like to become a penetration tester or work as a Cyber Security practioner, then learning how to use Wireshark is a must. There are a ton of resources out there to learn Wireshark, and, of particular interest, there's also a Wireshark Certification which you can achieve and place on your LinkedIn profile.


Aircrack-ng | Free
Password Cracking Tool

Aircrack-ng
The Aircrack suite of Wifi (Wireless) hacking tools are legendary because they are very effectively when used in the right hands. For those new to this wireless-specific hacking program, Aircrack-ng is an 802.11 WEP and WPA-PSK keys cracking hacking tool that can recover keys when sufficient data packets have been captured (in monitor mode). For those tasked with penetrating and auditing wireless networks Aircrack-ng will become your best friend. It's useful to know that Aircrack-ng implements standard FMS attacks along with some optimizations like KoreK attacks, as well as the PTW attacks to make their attacks more potent. If you are a mediocre hacker then youll be able to crack WEP in a few minutes and you ought to be pretty proficient at being able to crack WPA/ WPA2. For those interested in Wireless Hacking we'd also highly recommend taking a look at the very awesome Reaver, another very popular hacking tool that alas we couldn't add to our list.


Nikto Website Vulnerability Scanner | Free
Website Vulnerability Scanner Hacking Tool


Nikto logoNikto is another classic 'Hacking Tool' that a lot of pentesters like to use. Worth mentioning that Nickto is sponsored by Netsparker (which is yet another Hacking Tool that we have also listed in our directory). Nikto is an Open Source (GPL) web server scanner which is able to scan and detect web servers for vulnerabilities. The system searches against a database of over 6800 potentially dangerous files/ programs when scanning software stacks. Nikto, like other scanners out there, also scans for outdated (unpatched) versions of over 1300 servers, and version specific problems on over 275 servers. Interestingly, Nikto can also check server configuration items such as the presence of multiple index files, HTTP server options, and the platform will also try to identify installed web servers and web applications. Nikto will get picked up by any semi-decent IDS tool so its' really useful when conducting a white-hat/ white-box pentest. Certainly a great tool to learn your skills on when attacking an open box for training.

OWASP Zed | Free
Web Vulnerability Scanner

The Zed Attack Proxy (ZAP) is now one of the most popular OWASP projects. The fact that you've reached this page means that you are likely already a relatively seasoned cybersecurity professional so it's highly likely that you are very familiar with OWASP, not least the OWASP Top Ten Threats listing which is considered as being the 'guide-book' of web application security. This hacking and pentesting tool is a very efficient as well as being an 'easy to use' program that finds vulnerabilities in web applications. ZAP is a popular tool because it does have a lot of support and the OWASP community is really an excellent resource for those that work within Cyber Security. ZAP provides automated scanners as well as various tools that allow you the cyber pro to discover security vulnerabilities manually. Understanding and being able to master this tool would also be advantageous to your career as a penetration tester. If you are a developer then you have it's obviously highly recommended that you learn how to become very proficient with this 'hacker tool!'


Cain and Abel Hacking Tool | Free
Password Cracker/ Password Hacking

Cain and Abel (often simply abbreviated to Cain) is a hugely popular hacking tool and one that is very often mentioned online in a variety of 'hacking tutorials'. At its' heart, Cain and Abel is a password recovery tool for Microsoft Windows but it can be used off-label in a variety of uses, for example, white and black hat hackers use Cain to recover (i.e. 'crack') many types of passwords using methods such as network packet sniffing and by using the tool to crack password hashes. Cain, for example, when used to crack password hashes would use methods such as dictionary attacks, brute force, rainbow table attacks and cryptanalysis attacks,sniffer attacks, man in the middle attacks


BeEF | Free
BeEF is short for The Browser Exploitation Framework. It is a penetration testing tool that focuses on the web browser.


Amid growing concerns about web-borne attacks against clients, including mobile clients, BeEF allows the professional penetration tester to assess the actual security posture of a target environment by using client-side attack vectors. Unlike other security frameworks, BeEF looks past the hardened network perimeter and client system, and examines exploitability within the context of the one open door: the web browser. BeEF will hook one or more web browsers and use them as beachheads for launching directed command modules and further attacks against the system from within the browser context.


Sqlmap | Free

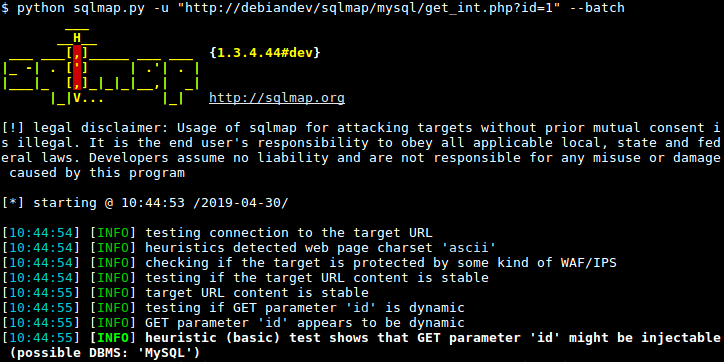
Sqlmap is an open source penetration testing tool that automates the process of detecting and exploiting SQL injection flaws and taking over of database servers. It comes with a powerful detection engine, many niche features for the ultimate penetration tester and a broad range of switches lasting from database fingerprinting, over data fetching from the database, to accessing the underlying file system and executing commands on the operating system via out-of-band connections.

How to install All Kali Linux Tools Using “Katoolin” on Debian/Ubuntu


Katoolin is a script that helps to install Kali Linux tools on your Linux distribution of choice. For those of us who like to use penetration testing tools provided by Kali Linux development team can effectively do that on their preferred Linux distribution by using Katoolin.
In this tutorial we are going to look at steps to install Katoolin on Debian based derivatives.

Major Features of Katoolin

  1. Adding Kali Linux repositories.
  2. Removing Kali Linux repositories.
  3. Installing Kali Linux tools.

Requirements

Requirements for installing and using Katoolin.
  1. An operating system for this case we are using Ubuntu 14.04 64-bit.
  2. Python 2.7

Installing Katoolin

To install Katoolin run the following commands.
# apt-get install git
# git clone https://github.com/LionSec/katoolin.git && cp katoolin/katoolin.py /usr/bin/katoolin

OUTPUT

cp katoolin/katoolin.py /usr/bin/katoolin
Cloning into 'katoolin'...
remote: Counting objects: 52, done.
remote: Total 52 (delta 0), reused 0 (delta 0), pack-reused 52
Unpacking objects: 100% (52/52), done.
Checking connectivity... done.

Then make /usr/bin/katoolin executable by running the command below.

# chmod +x /usr/bin/katoolin

Now you can run Katoolin as follows.
# katoolin
The output below shows the interface of Katoolin when you run the command.
As you can see it provides a menu from which you can make selections of what you want to do.
Incase the above way of installation fails, you also can try the following steps.
Go to https://github.com/LionSec/katoolin.git page download the zip file and extract it.
# wget https://github.com/LionSec/katoolin/archive/master.zip
# unzip master.zip
After extracting, you should be able to find katoolin.py script. Run katoolin.py command, you will be able to view the output similar to above.
# cd katoolin-master/
# chmod 755 katoolin.py
#  ./katoolin.py 

How do I use Katoolin?

To add Kali Linux repositories and update repositories, select option 1 from the Menu.
1) Add Kali repositories & Update 
2) View Categories
3) Install classicmenu indicator
4) Install Kali menu
5) Help
kat > 1
1) Add kali linux repositories
2) Update
3) Remove all kali linux repositories
4) View the contents of sources.list file
What do you want to do ?> 1
Sample Output
Executing: gpg --ignore-time-conflict --no-options --no-default-keyring --homedir /tmp/tmp.DC9QzwECdM --no-auto-check-trustdb --trust-model always --keyring /etc/apt/trusted.gpg --primary-keyring /etc/apt/trusted.gpg --keyserver pgp.mit.edu --recv-keys ED444FF07D8D0BF6
gpg: requesting key 7D8D0BF6 from hkp server pgp.mit.edu
gpg: key 7D8D0BF6: public key "Kali Linux Repository <devel@kali.org>" imported
gpg: Total number processed: 1
gpg:               imported: 1  (RSA: 1)
Then you can select option 2 from the interface above to update the repositories. From the output below, I have only captured a portion where Kali Linux repositories are being updated so that one can install Kali Linux tools in Ubuntu.
What do you want to do ?> 2
Ign http://in.archive.ubuntu.com vivid InRelease                                                                                            
Ign http://security.ubuntu.com vivid-security InRelease                                                                                                               
Ign http://in.archive.ubuntu.com vivid-updates InRelease                                                                                                               
Get:1 http://security.ubuntu.com vivid-security Release.gpg [933B]                                                                                                    
Ign http://in.archive.ubuntu.com vivid-backports InRelease                                                                                                                      
Get:2 http://repo.kali.org kali-bleeding-edge InRelease [11.9 kB]                                                                              
Get:3 http://security.ubuntu.com vivid-security Release [63.5 kB]                                                            
Hit http://in.archive.ubuntu.com vivid Release.gpg                                                                              
Get:4 http://repo.kali.org kali-bleeding-edge/main amd64 Packages [8,164 B]                                                
Get:5 http://in.archive.ubuntu.com vivid-updates Release.gpg [933 B]                                                                
Get:6 http://repo.kali.org kali-bleeding-edge/main i386 Packages [8,162 B]                                               
Hit http://in.archive.ubuntu.com vivid-backports Release.gpg    
...  
If you want to delete the Kali Linux repositories you added, then select option 3.
What do you want to do ?> 3
All kali linux repositories have been deleted !
As part of its operation, the Apt package uses a /etc/apt/sources.list that lists the ‘sources‘ from which you can obtain and install other packages.
To view contents of /etc/apt/sources.list file, select of 4.
What do you want to do ?> 4
#deb cdrom:[Ubuntu 15.04 _Vivid Vervet_ - Release amd64 (20150422)]/ vivid main restricted
# See http://help.ubuntu.com/community/UpgradeNotes for how to upgrade to
# newer versions of the distribution.
deb http://in.archive.ubuntu.com/ubuntu/ vivid main restricted
deb-src http://in.archive.ubuntu.com/ubuntu/ vivid main restricted
## Major bug fix updates produced after the final release of the
## distribution.
deb http://in.archive.ubuntu.com/ubuntu/ vivid-updates main restricted
deb-src http://in.archive.ubuntu.com/ubuntu/ vivid-updates main restricted
...
To go back you can simply type back and press [Enter] key.
What do you want to do ?> back
1) Add Kali repositories & Update 
2) View Categories
3) Install classicmenu indicator
4) Install Kali menu
5) Help
kat > 
To go back to the main menu, simply type gohome and press [Enter] key.
kat > gohome
1) Add Kali repositories & Update 
2) View Categories
3) Install classicmenu indicator
4) Install Kali menu
5) Help
kat >
There are different categories of Kali Linux tools you can install on your Ubuntu using Katoolin.
To view the available categories, select option 2 from the main menu.
kat > 2
**************************** All Categories *****************************
1) Information Gathering   8) Exploitation Tools
2) Vulnerability Analysis   9) Forensics Tools
3) Wireless Attacks    10) Stress Testing
4) Web Applications    11) Password Attacks
5) Sniffing & Spoofing    12) Reverse Engineering
6) Maintaining Access    13) Hardware Hacking
7) Reporting Tools     14) Extra
0) All
Select a category or press (0) to install all Kali linux tools .
You can select a category of choice or install all available Kali Linux tools by selecting option (0) and press[Enter] to install.
You can also install a ClassicMenu indicator using Katoolin.
    1. ClassicMenu Indicator is a application indicator for the top panel of Ubuntu’s Unity desktop environment.
    2. ClassicMenu Indicator provides a simple way for you to get a classic GNOME-style application menu for those who prefer this over the default Unity dash menu.
To install classicmenu indicator, press y and press [Enter].
kat > back
1) Add Kali repositories & Update 
2) View Categories
3) Install classicmenu indicator
4) Install Kali menu
5) Help
kat > 3
ClassicMenu Indicator is a notification area applet (application indicator) for the top panel of Ubuntu's Unity desktop environment.
It provides a simple way to get a classic GNOME-style application menu for those who prefer this over the Unity dash menu.
Like the classic GNOME menu, it includes Wine games and applications if you have those installed.
For more information , please visit : http://www.florian-diesch.de/software/classicmenu-indicator/
Do you want to install classicmenu indicator ? [y/n]> y
This PPA contains the most recent alpha/beta releases for
 * Arronax http://www.florian-diesch.de/software/arronax/
 * ClassicMenu Indicator http://www.florian-diesch.de/software/classicmenu-indicator/
* Privacy Indicator http://www.florian-diesch.de/software/indicator-privacy/
 * RunLens http://www.florian-diesch.de/software/runlens/
 * Unsettings http://www.florian-diesch.de/software/unsettings/
 * UUdeLens http://www.florian-diesch.de/software/uudelens
More info: https://launchpad.net/~diesch/+archive/ubuntu/testing
Press [ENTER] to continue or ctrl-c to cancel adding it
gpg: keyring `/tmp/tmpaqk6fphl/secring.gpg' created
gpg: keyring `/tmp/tmpaqk6fphl/pubring.gpg' created
...
You can also install Kali menu in Ubuntu by select option 4 and press y and then press [Enter].